Where Cloud Backups Live
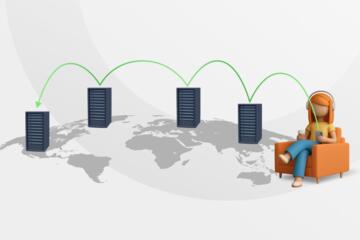
Cloud backup services store your data on provider-managed servers in data centers, not on your phone or computer. The “where” depends on the service’s storage regions, which are often selectable during setup or inferred from your account’s country and chosen plan.
Most providers separate data into multiple layers: object storage for file chunks, metadata storage for file names and versions, and key management for encryption. A common pattern uses deduplication, so identical blocks across files may be stored once, which changes how much data is actually written to storage. For example, if you back up a folder twice, the second run may upload fewer blocks because the service recognizes previously stored chunks.
Two evidence-based facts help ground expectations. First, many cloud backup systems use encryption in transit (for example, TLS) and encryption at rest (for example, AES-256 in common implementations), but the exact algorithm and key handling vary by provider. Second, file recovery often depends on metadata integrity; losing or corrupting metadata can prevent restoration even when some data blocks remain in storage.
Pain Points And Myths
People often assume “cloud backup” means “instant access to my files.” In practice, restore speed depends on how the provider stores versions, how many files changed, and whether the service supports partial restores or requires full rehydration.
Another common misunderstanding is that cloud backup equals cloud sync. Sync tools mirror files continuously, while backup tools typically keep historical versions and may use retention rules. If you delete a file and your sync service mirrors that deletion, you can lose the only copy unless version history exists. Backup services usually keep older versions, but retention windows differ by plan and settings.
Recovery also depends on authentication and authorization. If you lose access to the account, the provider may require identity verification before restoring data. If you use end-to-end encryption with a customer-held key, recovery can fail when the key is lost, even if the provider still has encrypted data.
Supporting technologies shape outcomes. Deduplication reduces storage and upload time, but it increases reliance on correct chunk indexing. Versioning creates multiple restore targets, and retention policies determine which versions remain. Some services use block-level storage and checksums; others use file-level snapshots. Those design choices affect what “restore” means when you request a specific date.
Solutions And Advice
Choose A Storage Region Plan
During setup, look for options that control the backup region or data residency. If the service offers region selection, pick one aligned with your legal and privacy needs. If it does not, check the provider’s documentation for where data is stored by default. For cross-border concerns, the provider’s privacy policy and terms usually describe data transfer mechanisms, but the exact data center locations may not be listed.
After setup, confirm the account’s backup status and retention settings in the provider console. A retention setting like “keep versions for 30 days” changes recovery options more than most users expect. If the console shows “last successful backup” and “next scheduled backup,” treat those as operational signals, not marketing text.
Verify Encryption And Key Handling
Check whether the service uses encryption in transit and at rest, and whether it uses customer-managed keys or end-to-end encryption. If you see terms like “zero-knowledge” or “end-to-end,” read the recovery section carefully because key loss can make encrypted data unrecoverable. If the service uses provider-managed keys, recovery typically depends on account access rather than a separate key file.
Practical step: store recovery codes and keep a secure record of how to regain account access. For example, many services generate recovery codes during 2FA setup; losing those codes can delay restoration while identity verification runs. That delay is not a technical failure of storage, but it still blocks recovery.
Test A Restore Before You Need It
Run a small restore test on a non-critical folder. Pick a file type you can verify quickly, such as a PDF or a photo, and restore it to a different folder on the same device. Compare file hashes or at least file sizes and timestamps when the service shows them. Some clients offer “browse versions” so you can restore a specific point-in-time without rehydrating everything.
Do this test after major changes like switching computers, upgrading the backup agent, or changing retention. A mild frustration: restore tests often fail because users restore to the same path and the client refuses to overwrite existing files, which looks like a “missing backup” problem.
Plan For Device And Account Loss
Recovery differs for device loss versus account lockout. For device loss, you typically install the backup client on the new device, sign in, then trigger a restore. For account lockout, you may need to complete identity verification before the console allows restore actions.
For ransomware scenarios, confirm whether the service supports version rollback and whether it can restore deleted files from retention. If the provider offers “instant restore” or “file browsing,” test it with a harmless deletion in a controlled folder so you understand how quickly you can revert.
Realistic Scenario Examples
Scenario 1: Accidental deletion on a laptop. A user deletes a project folder and empties the recycle bin. The backup client had run successfully earlier that day, and retention kept 30 days of versions. The user restores the folder by browsing versions and selecting the last snapshot before deletion. The restore takes longer than expected because the folder contains many small files, and the client rehydrates chunks one by one.
Scenario 2: Key loss with end-to-end encryption. A user enables end-to-end encryption and stores the encrypted backup key on a phone that later fails. The provider still holds encrypted data, but the user cannot decrypt it without the key. The account login works, yet restore returns an error because decryption cannot proceed. The user must recover the key from a previously exported key file or recovery method, which highlights why key management steps matter.
Recovery Checklist
| Decision Point | What To Check | Why It Affects Recovery | What Good Looks Like |
|---|---|---|---|
| Retention | Version history length and deletion handling | Determines how far back you can restore | Clear retention window in the console |
| Encryption Model | Provider-managed vs customer-held keys | Key loss can block decryption | Documented key recovery steps |
| Restore Method | Browse versions vs full restore | Affects time and bandwidth use | Partial restore works for folders |
| Client Health | Agent version and last successful run | Prevents silent backup failures | Recent “last successful backup” timestamp |
Step-by-step checklist for a practical restore test: (1) pick a small folder with mixed file types, (2) confirm the last backup completed successfully, (3) delete the folder locally, (4) restore from the provider’s version browser, (5) verify file sizes or hashes, and (6) repeat after changing the backup agent or retention settings. If any step fails, treat it as a configuration issue rather than a storage mystery.
Mistakes That Break Trust
One mistake is assuming that “uploaded” means “recoverable.” Some clients show upload progress even when metadata updates fail, which can leave you with incomplete restore options. Another mistake is ignoring retention settings because the default plan may keep fewer versions than expected.
Users also confuse “cloud backup” with “cloud storage.” Storage services that sync files continuously do not automatically protect against ransomware encryption of the same files. Backup services that keep historical versions can help, but only when the retention window includes the pre-encryption state.
Another frequent error is restoring to the same location without checking overwrite behavior. Many clients either refuse to overwrite or create duplicates with suffixes, and the resulting confusion looks like missing data. A mild aside: I’ve seen people conclude “the backup is broken” after a restore because the restored files landed in a nested folder like “Restored (1)” and they never checked the full path.
FAQ
Do Cloud Backups Store Files In One Place?
Most services store data across multiple servers inside one or more storage regions. The exact data center locations usually depend on the provider’s infrastructure and your account’s region settings, which may be described at a high level in documentation.
How Does A Restore Rebuild My Files?
Recovery typically uses stored file metadata plus encrypted chunks or blocks. The service reconstructs the requested version, verifies integrity with checksums, then downloads the restored files to your device.
Why Does Restore Take Longer Than Upload?
Restore can require rehydrating many small chunks, validating integrity, and writing files to disk on your device. Upload may benefit from deduplication and parallel chunking, while restore often involves more reconstruction work.
What Happens If I Lose My Account Access?
Many providers require identity verification before enabling restore actions. If your encryption uses customer-held keys, recovery may also require the key or recovery codes, not just account login.
Can I Restore Only One Folder Or File?
Many backup services support browsing versions and restoring selected files or folders. Some plans or setups require a broader restore, so the console’s restore options and version browser behavior matter.
Author's Insight
Cloud backup recovery depends less on “where files are stored” and more on how the provider tracks versions, handles encryption keys, and reconstructs file chunks. Metadata integrity and retention rules often determine whether a restore works for a specific date. Encryption models change the recovery path: provider-managed keys usually tie recovery to account access, while end-to-end encryption ties recovery to key availability. A practical approach is to test a small restore after setup and after any retention or encryption changes, then confirm you can regain access through your chosen recovery methods.
Key Takeaways
Cloud backups store data on provider-managed servers in one or more storage regions, with metadata and encryption keys playing a central role in recovery. Recovery works by reconstructing requested versions from stored chunks and metadata, then downloading the result to your device.
Next steps: review retention and encryption settings, confirm the last successful backup, and run a small restore test that verifies file integrity. If you plan for device loss, confirm how the client re-authenticates and how restore behaves on a new machine.
Limits exist. Restore speed varies with file counts, chunking, and network conditions, and some failure modes involve account access or key loss rather than missing storage. If you suspect you have ransomware-encrypted files, restore from a pre-encryption version and keep the encrypted originals untouched until you confirm the restored copies.